A customer agrees to receive offers on a website, changes their preferences in a mobile app, yet the CRM and messaging provider continue using the previous settings. When a complaint arises, the business has to search through forms, activity records and emails across multiple departments.
For organizations operating multiple websites, apps, internal systems and external partner channels, consent management must cover the entire process: capturing choices, applying them in business operations and providing evidence when needed.
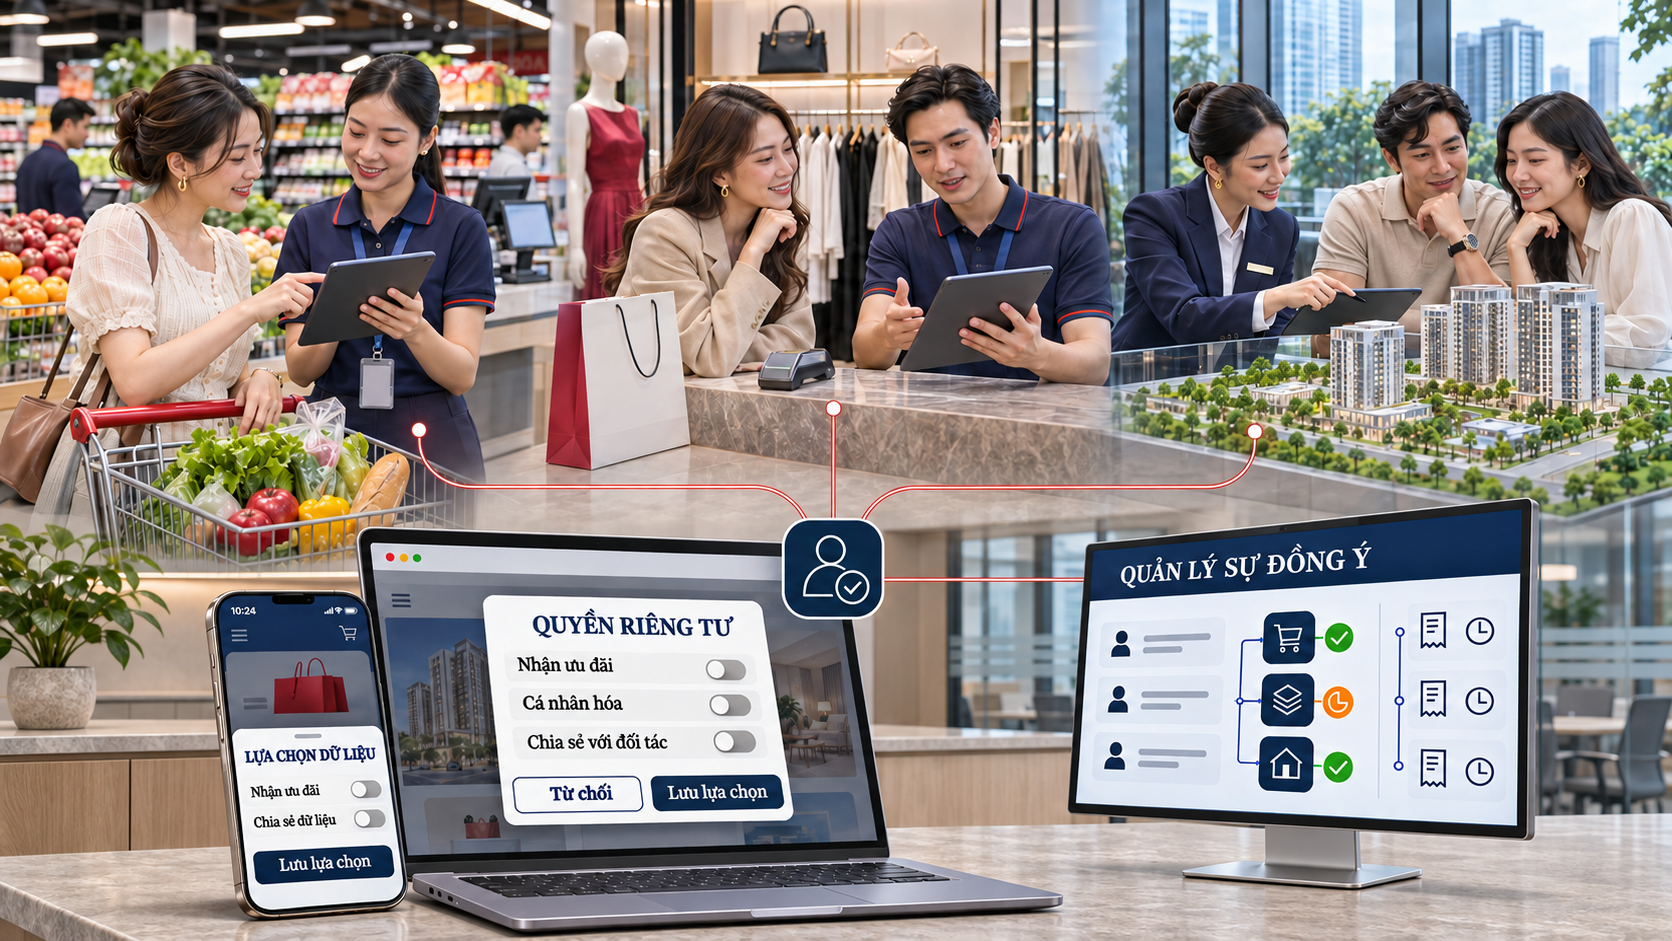
Smart Consent Management acts as a shared management layer connected to the systems a business already uses. A well-defined solution should cover eight functional areas.
1. Collect consent across multiple touchpoints
Capture choices through websites, mobile apps, service counters, employee portals and partner portals. Individuals can make separate choices for specific purposes, such as receiving marketing communications, personalizing their experience or sharing information with identified partners.
Different forms send records to a common platform, reducing inconsistent storage across applications. OneTrust’s technical documentation describes how external applications can submit consent transactions through APIs.
2. Maintain centralized consent profiles
Authorized users can look up a customer, employee or partner contact to see which purposes they have agreed to, where and when their choices were recorded, and their current status.
Profiles should clearly distinguish between consent given, declined, withdrawn and no evidence available. Linking identities across systems requires appropriate verification rules to prevent different individuals from being incorrectly merged because they share a phone number or device.
3. Let individuals manage their preferences
Provide a privacy preference center where individuals can review and change their choices: stop promotional emails, change communication channels or withdraw consent for a particular purpose.
When a request arrives through a call center or service counter, authorized staff can update the record through a verification process and retain supporting evidence. OneTrust also documents staff-assisted updates based on telephone calls or paper forms.
4. Synchronize choices with existing systems
Connect websites, apps, CRM platforms, marketing tools and other relevant systems through APIs, integration toolkits or event notifications.
For example, when a customer withdraws marketing consent in an app, the solution sends the updated status to the CRM and messaging platform. Receiving applications must be configured to check and apply the relevant preference before performing the corresponding activity. OneTrust documents SDK and REST API integration approaches for recording and updating these choices.
5. Track implementation and handle synchronization failures
Recording a request centrally does not, by itself, confirm that every connected system has completed the required action. The integration scope should therefore track which systems have received the update, applied it, remain pending or encountered an error.
For legacy applications without APIs, a managed task and completion-confirmation process may be required. External partners also need agreed mechanisms for receiving requests, carrying out actions and returning evidence of completion.
6. Trace changes and export supporting evidence
When a review is needed, authorized personnel can identify who made a choice, when, through which channel, for what purpose and under which version of the privacy notice.
The evidence record should link preference changes to downstream implementation results. OneTrust’s transaction APIs provide access to consent transactions, dates, purposes and associated preferences, supporting the development of evidence-retrieval functions.
7. Provide centralized administration and clear access controls
Responsible teams can manage purpose catalogs, privacy notice versions, forms and access permissions by role or legal entity.
An operational dashboard should highlight records without sufficient evidence, incomplete requests and failed integrations. When notices or purposes change, the system can help identify groups requiring review or renewed consent under approved rules.
8. Use AI to support review and operations
Depending on the implementation scope, AI capabilities can be added to suggest purpose classifications from forms, identify inconsistencies across channels, summarize a profile’s history or help investigate incomplete requests.
These capabilities require validation and appropriate access controls. AI must not infer that an individual has consented; the official status must remain grounded in recorded choices and supporting evidence.
A practical example
A customer turns off promotional communications in the app. The system records the withdrawal, updates the centralized profile, sends the change to the CRM and messaging platform, and tracks their responses. If an integration fails, the request is flagged for follow-up. When the customer asks for confirmation, the business can retrieve both the time of the change and the implementation results.
Where should a business start?
Start by identifying which systems process the data, their purposes and the departments responsible. Then prioritize a clearly defined flow, such as ## website/app → consent management → CRM → marketing platform, and test it thoroughly before expanding.
Not all personal data processing relies on consent. The legal team should determine the applicable grounds and rules before system configuration.
Metatek starts with the organization’s actual business processes and system landscape to propose appropriate functions, integrations and operational responsibilities. The intended value is less manual reconciliation, reduced reliance on outdated preferences and evidence-based answers to three questions: **For what purpose is this data being used? Which recorded choice supports that use? How has it been controlled?
References
OneTrust — Implementing the Collection Point with REST API OneTrust — Managing Consent on Behalf of a Data Subject OneTrust — Get List of Transactions NIST — Using Privacy Framework 1.1 These sources describe reference principles and technical mechanisms. Actual automation, AI capabilities and synchronization coverage depend on the selected platform and agreed integration scope.