Recovery must be demonstrated by the ability to resume real business operations.
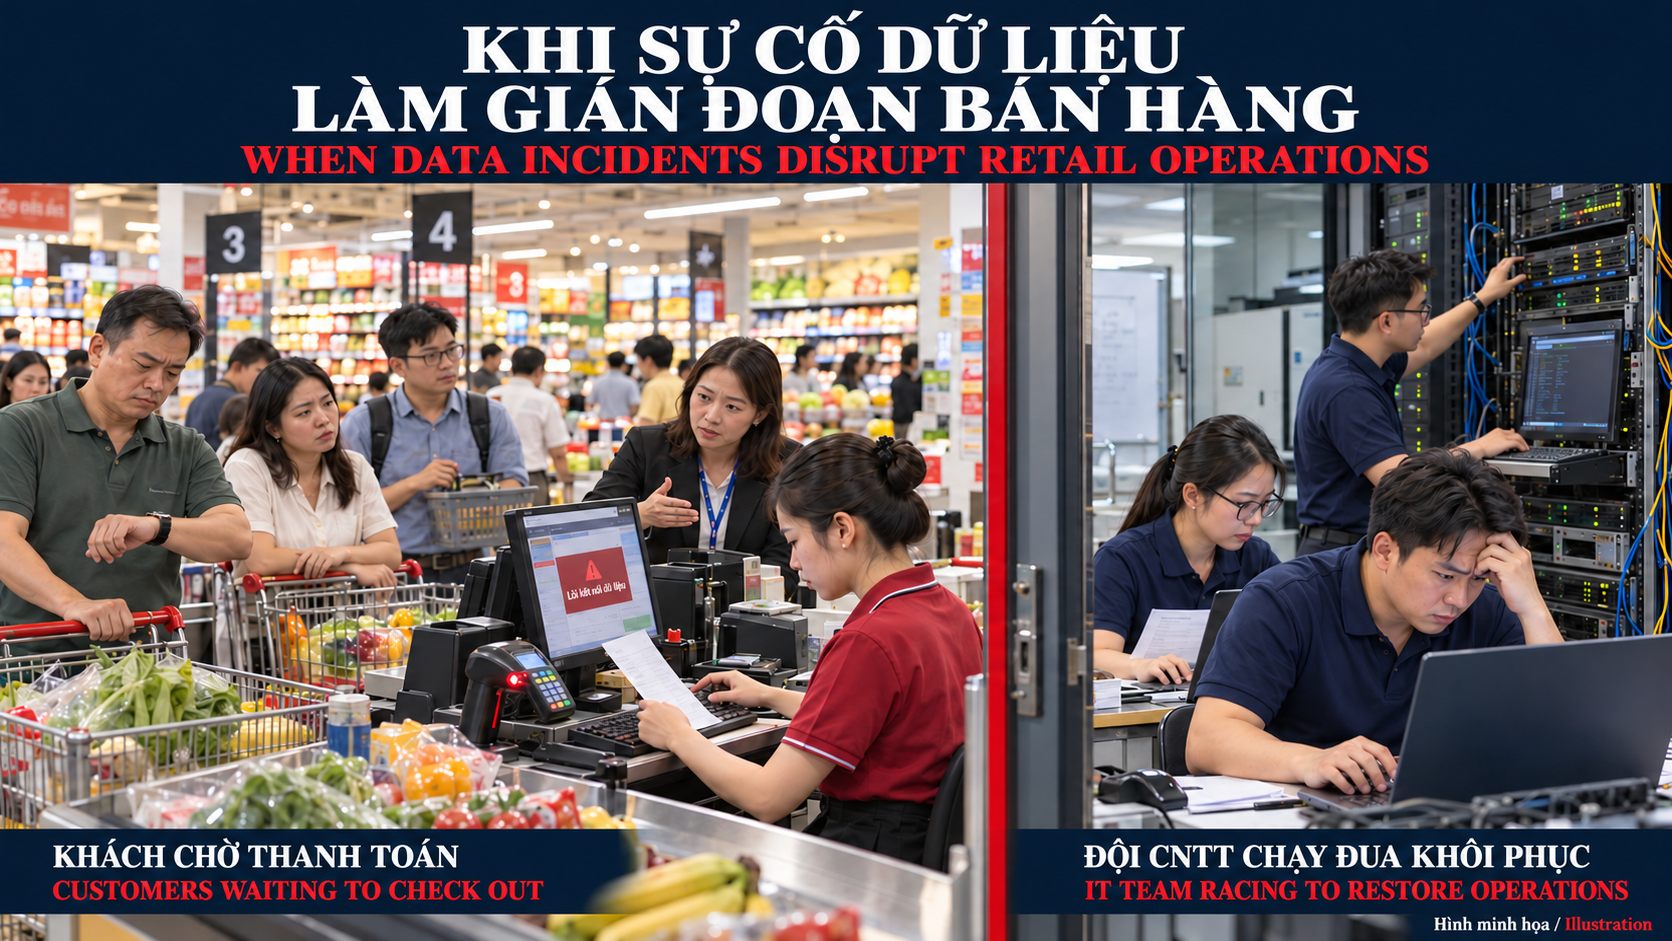
The backup completed successfully. Yet employees still cannot log in to the ERP system, inventory records are not updating, and orders are piling up.
This illustrates a critical distinction: recovering data is only part of restoring business operations. Applications, infrastructure and business processes must also work together again.
What does the evidence show?
Veeam’s 2026 survey covered more than 900 senior IT, security and risk leaders worldwide. Among ransomware victims whose data or operations were affected, only 28% reported fully recovering the affected data. This is a vendor-sponsored survey, not a statistic specific to Vietnam.
A 2026 academic review by Chun Yin Chiu, published in the International Journal of Critical Infrastructure Protection, highlights that manufacturing recovery depends on identity systems, applications, operational processes and supply chains. Restoring servers alone may not restore production.
Meanwhile, Timothy McIntosh and colleagues, reviewing 212 studies in ACM Computing Surveys, show that ransomware threats extend beyond encryption to data exfiltration. Backups do not, by themselves, resolve the consequences of stolen information.
Four questions businesses should verify
1. Which business processes must resume first?
Identify critical activities and their dependencies: identity services, networks, databases, applications and external partners.
2. How much disruption can the business tolerate?
Define the Recovery Time Objective (RTO)—the target time for restoring a service—and the Recovery Point Objective (RPO)—the maximum acceptable data loss measured in time. Set these for each critical business process.
3. Can the backups survive the same incident?
Assess backup separation, access controls and, where appropriate, protection against modification or deletion through immutable backups.
4. Has recovery been tested through real work?
Go beyond opening a restored file. Test user login, order creation, inventory updates and reconciliation. Record the actual recovery time and any unresolved gaps.
The UK’s National Cyber Security Centre (NCSC) recommends testing restoration regularly, documenting system dependencies and prioritising essential services during recovery.
Metatek’s approach
Metatek starts by understanding the business’s critical processes, existing infrastructure and acceptable downtime. This provides the basis for recommending backup, recovery and testing arrangements suited to its operational needs and resources.
What matters is demonstrable recovery: data can be restored, systems function, and employees can resume their work.
References and source assessment
[1] Veeam — Data Trust and Resilience Report 2026. A global vendor survey; useful industry evidence, with findings interpreted within the surveyed population.
[2] Chun Yin Chiu (2026) — From backup restoration to Minimum Viable Factory Recovery. An academic review focused on manufacturing recovery. The proposed framework requires further empirical validation.
[3] McIntosh et al. (2024) — Ransomware Reloaded. An academic review published in ACM Computing Surveys, examining ransomware research and mitigation in the era of data exfiltration.
[4] NCSC — Prepare technical recovery. Practical guidance from the UK’s national cybersecurity authority.