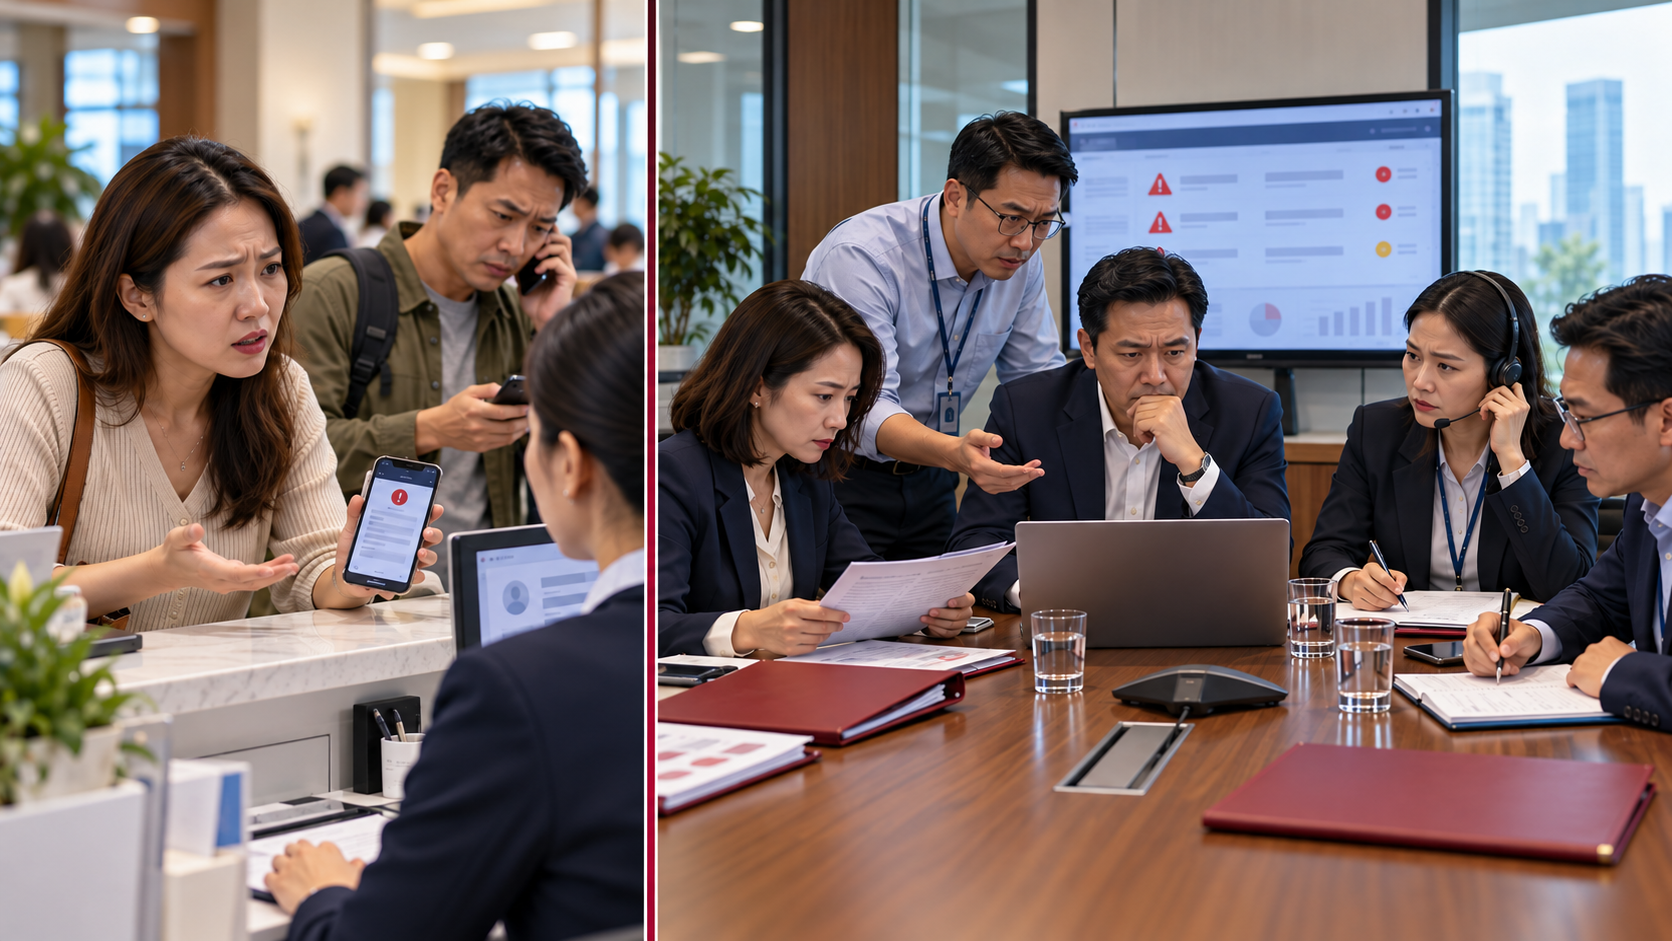
A customer reports that a stranger knows their order details. An employee discovers a membership list in a publicly shared folder. A supplier reports signs of unusual activity involving a support account.
These are illustrative scenarios for which businesses should prepare response plans. Initial signs are not enough to determine the full scope of an incident, but they need to be received, documented and assessed promptly.
While information remains incomplete, businesses can easily encounter two problems: multiple departments responding without a coordinator, or everyone waiting for technical findings before starting other tasks.
Metatek recommends organizing five workstreams in parallel, with priorities adjusted according to the actual impact.
1. ACTIVATE A COORDINATION LEAD AND CLARIFY RESPONSIBILITIES
As soon as information is received, businesses need to identify the person responsible for intake and coordination under the agreed procedure. This lead consolidates information on the situation, assigns tasks, tracks decisions and reports to the appropriate authority.
Participants typically include the information technology department, personnel responsible for data protection, legal, business operations, customer service and relevant suppliers.
It is important to clarify who conducts the technical assessment, who identifies the affected data, who reviews obligations and who approves information for external disclosure.
Defining responsibilities early can reduce the effort spent contacting multiple points of contact and limit inconsistent instructions.
2. LIMIT RISKS WHILE PRESERVING EVIDENCE
The technical team needs to assess appropriate containment measures: restricting access permissions, revoking shared links, addressing at-risk accounts or isolating affected components within the approved scope.
Alongside containment, information needed for verification should be documented:
When and how signs of unusual activity were detected.
The systems, accounts or suppliers involved.
The types of data suspected to be affected.
The actions taken and the people who performed them.
System logs, emails and supplier notifications need to be preserved, with appropriate access controls. Guidance from the Ministry of Public Security also cautions against deleting evidence without authorization when a data incident occurs.
Rapid recovery needs to go hand in hand with the ability to verify what happened. Deleting data or reinstalling systems before an assessment may destroy information needed to understand the cause and scope of the impact.
3. REVIEW NOTIFICATION OBLIGATIONS FROM THE OUTSET
Notification obligations need to be assessed in parallel with the technical response.
For entities and cases covered by Clause 1, Article 23 of the Law on Personal Data Protection, the deadline for notifying the specialized authority is no later than 72 hours after detecting a violation. A processor that detects a violation must promptly notify the personal data controller or the personal data controller and processor.
Businesses also need to review other obligations that may arise at the same time. The Ministry of Public Security notes that an attack on an information system that creates a risk to the security of customer information under Clause 3, Article 19 of the Law on Protection of Consumer Rights carries a 24-hour notification deadline.
Therefore, businesses should not assume that every incident has the same deadline. The responsible department needs to correctly identify the relevant role, applicable conditions, recipients and notification content, and clearly document the assessment process rather than waiting for a complete investigation report before starting the review.
4. RESPOND CONSISTENTLY AND FOCUS ON CUSTOMER INTERESTS
When customers get in touch, inconsistent answers can create additional concern. Businesses need to prepare guidance so that employees handling reports know which information has been verified and which issues need to be referred to the responsible point of contact.
Metatek recommends clearly distinguishing three categories of information: what is known, what is being checked and what action is being taken.
Businesses should not claim that “no data has been affected” without sufficient evidence. At the same time, they should avoid collecting or sharing unnecessary additional personal data while handling reports.
Information provided to customers and stakeholders needs to be appropriately scoped, approved and consistent with applicable obligations. This approach supports clear responses and reduces the need for customers to explain their situation repeatedly across multiple channels.
5. RESTORE OPERATIONS IN A CONTROLLED MANNER AND ADDRESS THE CAUSES
Restoring system operations does not mean that all response activities are complete. Businesses need to assess recovery conditions, check access permissions and monitor for continuing signs of unusual activity.
After an incident, businesses should review the factors that slowed the response: missing logs, difficulty contacting suppliers, unclear approval authority or a lack of guidance for employees.
NIST SP 800-61 Rev. 3 places incident response within cybersecurity risk management, linking preparation with detection, response and recovery. [3]
Based on this approach, businesses can turn post-incident findings into specific improvement tasks, with assigned owners and scheduled follow-up reviews.
PREPARE IN ADVANCE FOR MORE PROACTIVE COORDINATION
A practical response plan can start with a contact list, a responsibility chart, documentation templates and guidance for common scenarios. Exercises can then be conducted to test coordination capabilities.
Metatek works with businesses to review their current state, develop scenarios and standardize procedures, in coordination with the appropriate technical, operational and legal points of contact.
The aim is to reduce confusion, limit overlapping work and provide a basis for informed decisions. When each party clearly understands its role, businesses are better positioned to control incidents and maintain trust in customer relationships.
ASSESS YOUR RESPONSE READINESS WITH Metatek →
REFERENCES
[1] Law on Personal Data Protection No. 91/2025/QH15 — Article 23, version published in the Official Gazette.
[2] Ministry of Public Security — Warning of the risk of cybersecurity law violations by businesses and household businesses during digital transformation.
[3] NIST SP 800-61 Rev. 3 — Incident Response Recommendations for Cybersecurity Risk Management.
This content provides general guidance on governance and coordination. Notification obligations and response measures need to be determined for each specific incident.