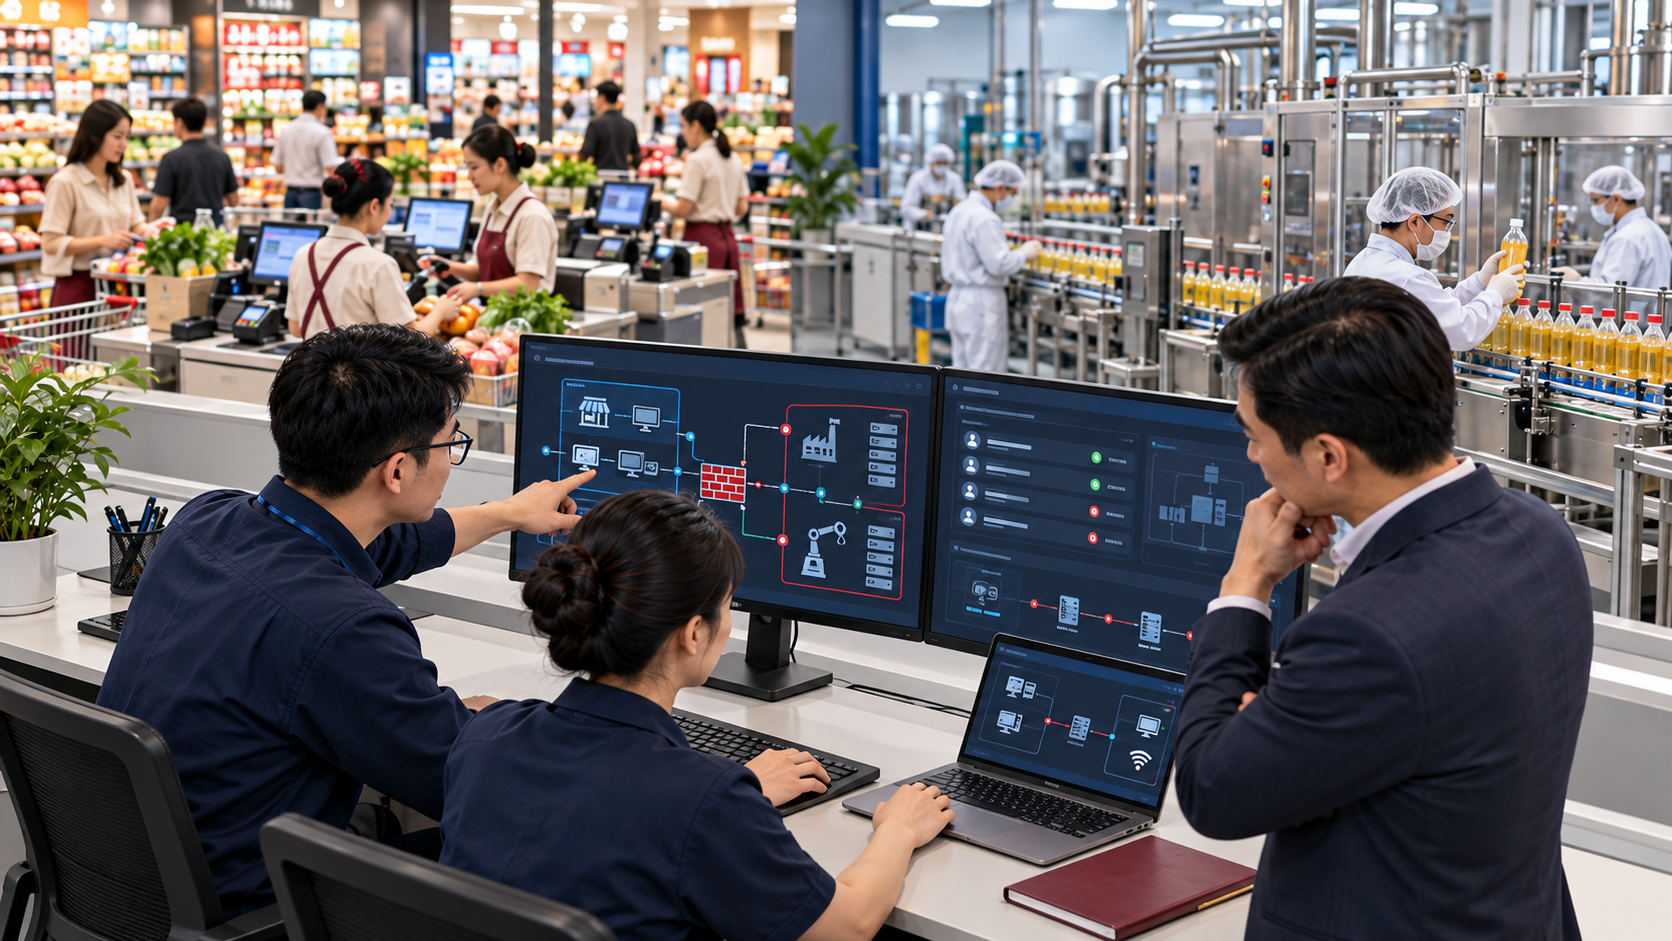
A business may simultaneously operate a sales website, management systems, HR software, customer databases and applications connected to suppliers. Each system serves different business functions, processes different data and has a different level of impact when an incident occurs.
Therefore, choosing protection solutions should begin with these questions: whom does the system serve, what information does it process, and what consequences could arise if it is disrupted or compromised?
These are also the issues businesses need to review when updating their practices to reflect the new cybersecurity legal framework.
THE LEGAL FRAMEWORK HAS CHANGED AS OF 2026
The Law on Cybersecurity No. 116/2025/QH15, effective from 01/07/2026, replaces the 2015 Law on Cyberinformation Security and the 2018 Law on Cybersecurity. Therefore, when developing compliance plans, businesses need to use the correct legal provisions currently in force. [1]
For information system protection, Decree 331/2026/NĐ-CP, effective from 19/08/2026, provides detailed regulations on level classification, implementation procedures and related protection requirements. [2]
Updating the legal basis enables businesses to review the appropriate scope of work and avoid applying the entire set of old requirements to systems whose scale or operating model has changed.
LEVELS ARE DETERMINED FOR EACH SYSTEM
A business may manage multiple systems at different levels. Classification needs to consider functions, information processed, users served, scope of impact and applicable criteria.
The software name, investment value or number of employees alone is not enough to determine a level.
For example, an internal system that handles only public information has different characteristics from a platform that provides online services and processes large volumes of customer data. The two systems need to be assessed according to their actual scope.
A QUICK GUIDE TO THE 5 INFORMATION SYSTEM LEVELS
The table below summarizes selected identifying characteristics under Decree 331/2026/NĐ-CP; it does not replace a full review of the criteria and procedures for determining levels.
Level
Selected identifying characteristics
Level 1
Systems serving internal purposes and processing only public information.
Level 2
Includes internal systems that process private information and personal information but do not process state secrets; certain online service systems and infrastructure belonging to an organization.
Level 3
Includes certain online services in conditional business sectors, online services that meet prescribed data thresholds and other specialized systems.
Level 4
Includes certain nationwide infrastructure, control systems for Grade I construction works and systems that meet the corresponding criteria for a high level of protection.
Level 5
Includes strategic systems, data of exceptional national importance, special-grade construction works or systems that meet the corresponding criteria.
Specific criteria also depend on the type of system, information and scope of service. [3]
DATA THRESHOLDS ARE A KEY CONSIDERATION FOR BUSINESSES
For the specified category of other online services, thresholds of at least 100,000 basic personal data subjects or at least 10,000 sensitive personal data subjects are criteria to consider for Level 3. These figures refer to the number of data subjects within the applicable scope, not the number of transactions or data rows. [3][4]
Retailers, e-commerce businesses and customer platform operators should monitor changes in data volume, user groups and the scope of connections.
When a system simultaneously meets criteria for multiple levels, the regulations require selecting the highest applicable level. Artificially splitting systems to reduce protection requirements is also strictly prohibited. [4]
PROTECTION REQUIREMENTS MUST MATCH THE LEVEL
Under the approach set out in the Law, entities responsible for Level 1–2 systems proactively select appropriate measures; implementation still requires a full review of all applicable requirements.
For Level 3–4 systems that are not on the list of information systems important to national security, basic measures include internal regulations, technical standards, firewalls, backups, monitoring and incident response. Information systems important to national security are subject to a separate, stricter protection regime. [5]
From an implementation perspective, Metatek recommends that businesses assess three factors together: the requirements to be met, existing capabilities and gaps to be addressed. This approach provides a basis for prioritizing budgets and making effective use of solutions already in place.
SYSTEMS WITH EXISTING DOCUMENTATION STILL NEED TO BE REVIEWED
The Law includes transitional provisions for systems that have already been assigned a level: they retain their assigned level and must meet the corresponding requirements under the new framework within the prescribed period.
For systems already under investment or construction before 01/07/2026, Decree 331 also includes separate transitional provisions. Businesses need to correctly identify each system's status to develop an implementation plan. [1][4]
Documentation should be reviewed alongside current operations. Expanding applications, changing data, connecting additional partners or switching infrastructure models may introduce issues that need to be reassessed.
WHERE SHOULD BUSINESSES START?
Metatek recommends four groups of tasks to develop an appropriate plan:
Create an inventory of systems and responsible contacts. Clarify functions, data, users, operating entities and key connections.
Review the basis for level classification. Compare the current state with the criteria, existing documentation and any changes that have occurred.
Assess protection gaps. Review access rights, backup and recovery, monitoring, response procedures and supplier responsibilities.
Develop a prioritized roadmap. Assign responsible personnel, identify resources and verify implementation results; coordinate with qualified specialist organizations for work subject to corresponding requirements.
The intended outcome is a protection plan that can be implemented and maintained, aligned with the business's actual operations.
METATEK SUPPORTS YOU FROM CURRENT-STATE ASSESSMENT TO A SUITABLE PLAN
Metatek works with businesses to clarify the systems currently in operation, their dependencies and the risks affecting business activities. From there, it coordinates with technical and legal contacts and appropriate specialist organizations to develop a plan.
The goal is to proactively address protection requirements, focus resources and reduce costly adjustments after systems have gone live.
DISCUSS YOUR SYSTEMS' CURRENT STATE AND LEVELS WITH METATEK →
REFERENCES
[1] Law on Cybersecurity No. 116/2025/QH15 — particularly Article 8, Article 10, Article 44 and Article 45.
[2] Decree 331/2026/NĐ-CP — Government Legal Documents Portal.
[3] Government News — Cybersecurity protection measures for information systems.
[4] Ministry of Public Security — New regulations on cybersecurity protection for information systems.
[5] Government Portal — New provisions in the Law on Cybersecurity No. 116/2025/QH15.
Updated based on sources cross-checked on 28/10/2026. This content is for reference only; specific levels and obligations must be determined based on the actual systems, applicable legal documents and the proper authority.